
WebReports runs under an IIS worker process. That process needs Windows file-system access to the application folder so WebReports can use its files, create application logs, and save uploaded branding images.
For the supported procedure in this article, grant the local IIS_IUSRS group Allow → Full control on the actual WebReports application folder and its subfolders and files. Complete this step before first launch in Configure IIS and Deploy WebReports.
Use the WebReports directory, not its parent C:\inetpub, a drive root, or another website's folder. The demo path in this article is C:\inetpub\WebReportsDemo; substitute the site's real physical path.
What the Permission Does
| Item | Purpose |
|---|---|
| IIS_IUSRS | The local IIS worker-process group used by this procedure. This is a Windows group, separate from users and roles managed inside WebReports. |
| Full control | Includes reading, creating, changing, and deleting files and folders, as well as changing permissions and taking ownership. It is the supported permission level for this procedure, not just a Read or Write selection. |
| Folder scope | Apply the grant to the WebReports application folder and its contents. Keeping the target specific avoids extending this grant to unrelated websites or other server directories. |
Group spelling: Enter IIS_IUSRS exactly. It is not IIS_Users or IUSR.
Confirm the Website and Worker Process
- Open IIS Manager and select the WebReports site under Sites.
- Open Basic Settings. Record the site's Physical path and assigned Application pool.
- Select Application Pools, select that pool, and open Advanced Settings.
- Review Process Model → Identity. The demo pool is named WebReports and uses ApplicationPoolIdentity.
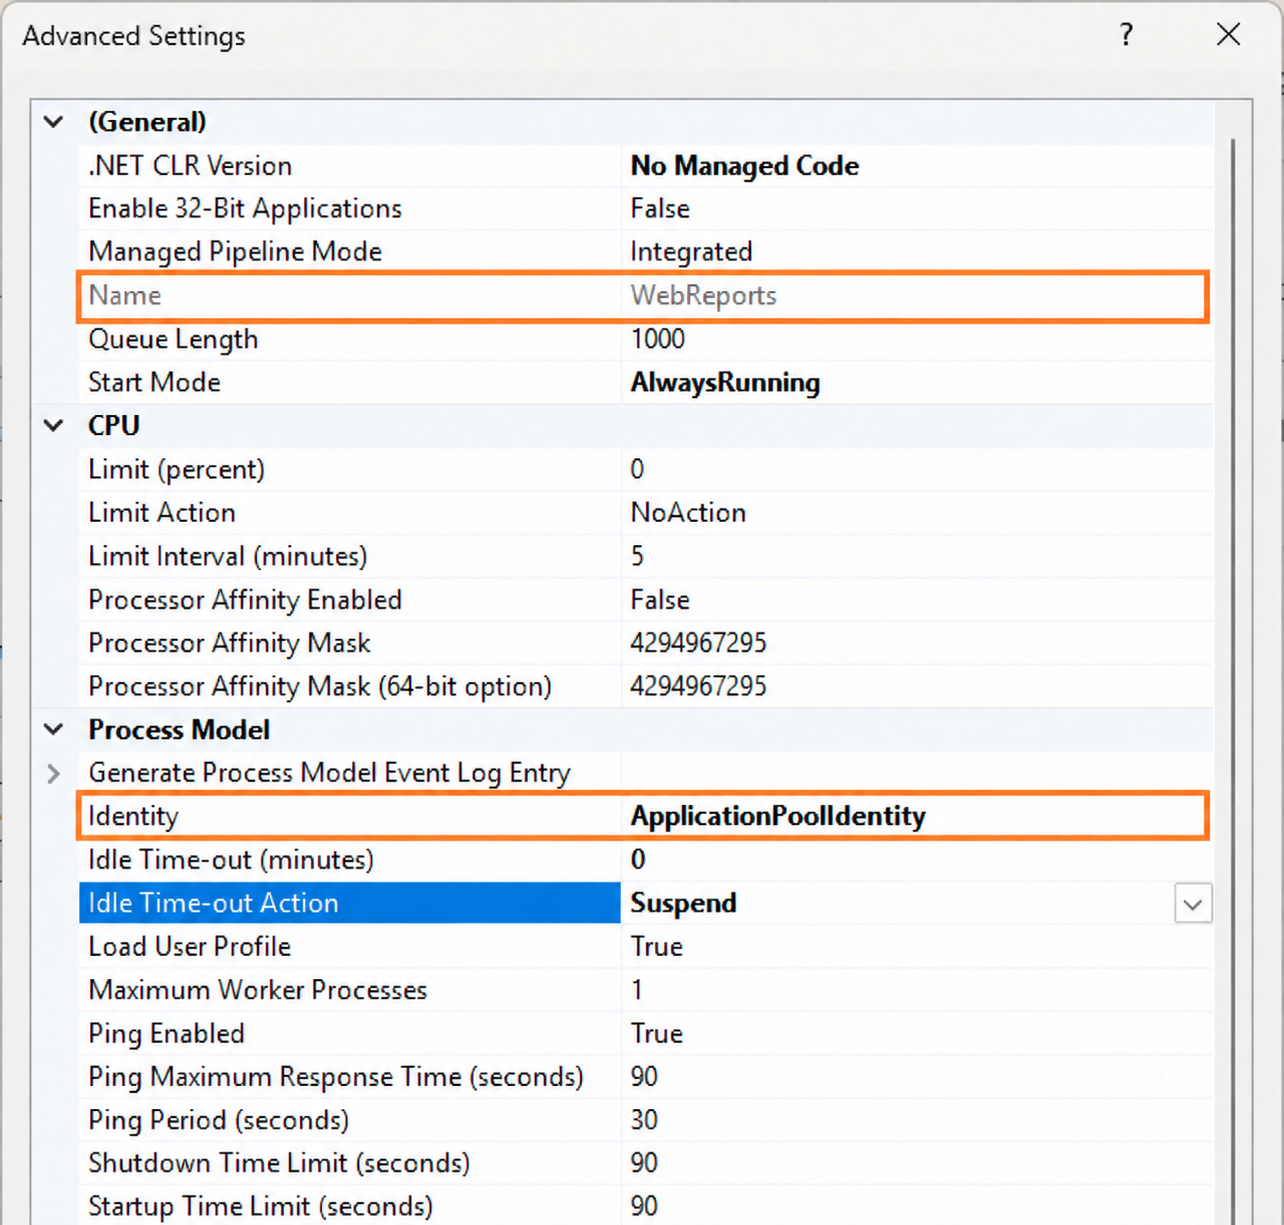
Edited demo reference: check the pool assigned to the actual WebReports site, then review its Identity. Other pictured settings are not additional permission instructions. Select the image to view it at full size.
With the normal IIS worker-process configuration, IIS includes the IIS_IUSRS group in the worker-process token. A pool using ApplicationPoolIdentity also has a pool-specific identity, such as IIS AppPool\WebReports. This article uses the confirmed IIS_IUSRS group grant; it does not require changing the pool identity or creating a Windows user.
For a custom service account or nonstandard group-membership configuration, have the deployment administrator confirm the effective worker access. See Microsoft's Understanding identities in IIS and Application Pool Identities.
Demo image context: Images are edited Windows/IIS reference illustrations using WR-DEMO-SRV, WebReportsDemo, and demo account labels. They show the controls and intended choices; they are not fresh captures of permissions applied to a server. Select an image to view it at full size.
Locate the WebReports Application Folder
- Open File Explorer on the server.
- Browse to the Physical path recorded from the site's Basic Settings. For the demo, this is
C:\inetpub\WebReportsDemo. - Right-click that application folder and select Properties.
- Open the Security tab and select Edit. Use an account authorized to manage permissions on that folder.
C:\inetpub\wwwroot is a common IIS directory, but use it only if it is the configured WebReports physical path. A custom site can use a different folder.
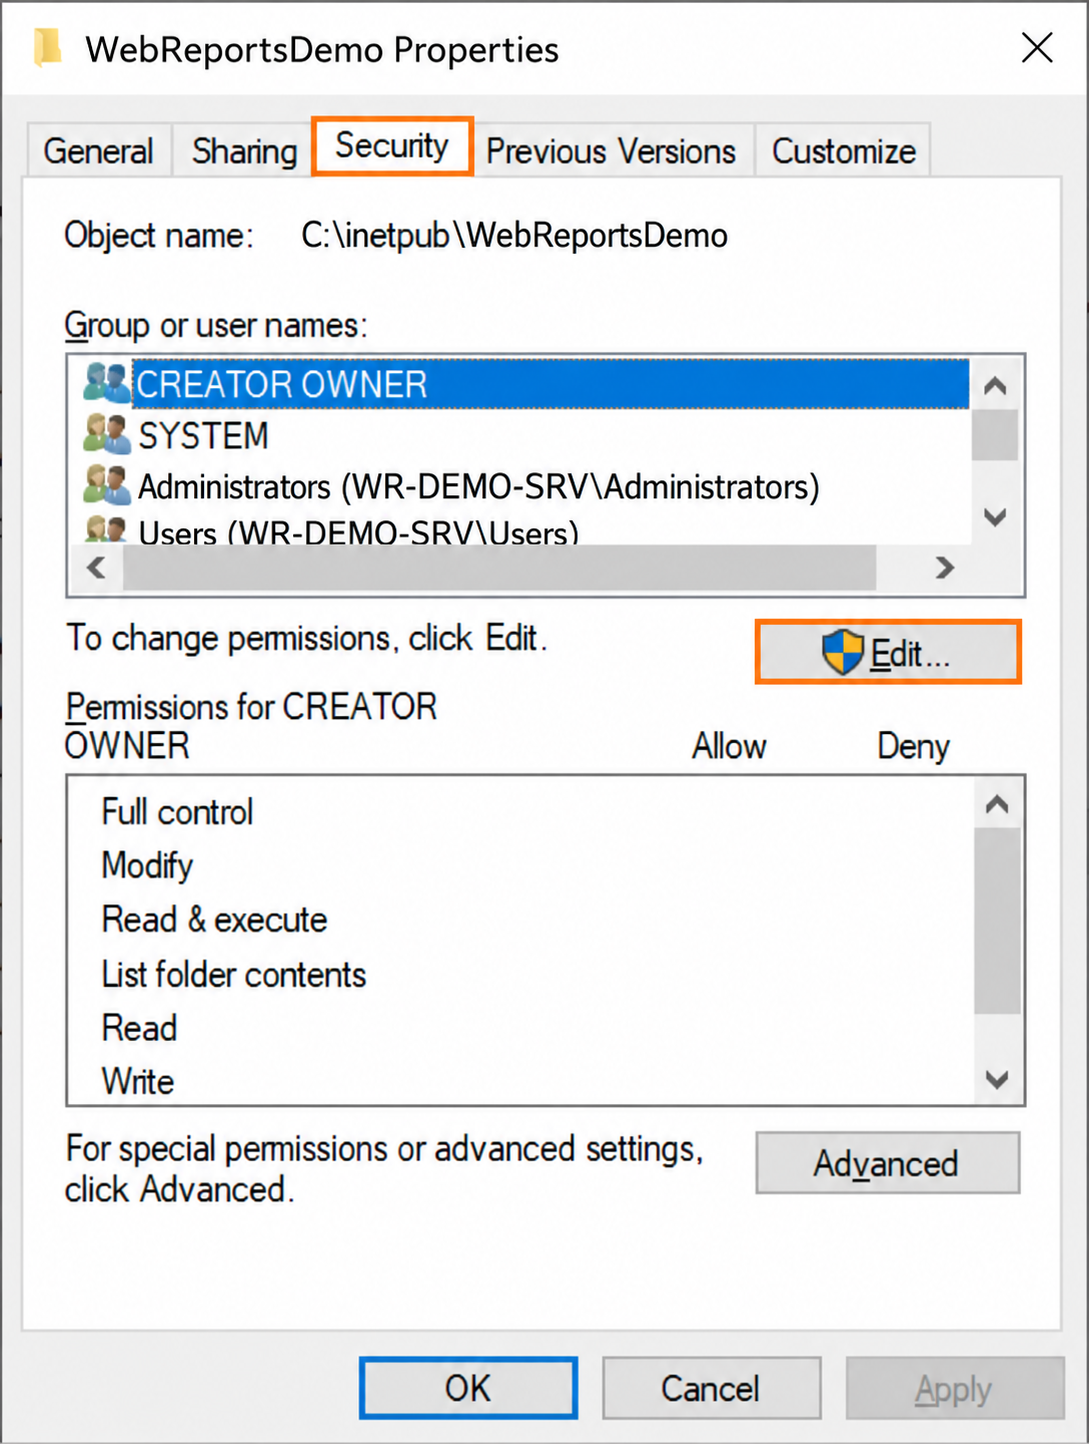
Edited demo reference: open the Security tab for the site's actual physical directory and select Edit. IIS_IUSRS is selected in a later step. Select the image to view it at full size.
Add IIS_IUSRS
- In the folder's permissions window, select Add. If the local IIS_IUSRS group is already listed, select it and continue to Configure Permissions.
- In Select Users or Groups, select Locations and choose the Windows Server that hosts the WebReports folder. The demo location is WR-DEMO-SRV.
- In Enter the object names to select, enter
IIS_IUSRS. - Select Check Names and confirm Windows recognizes the local group.
- Select OK to return to the folder's permissions window.
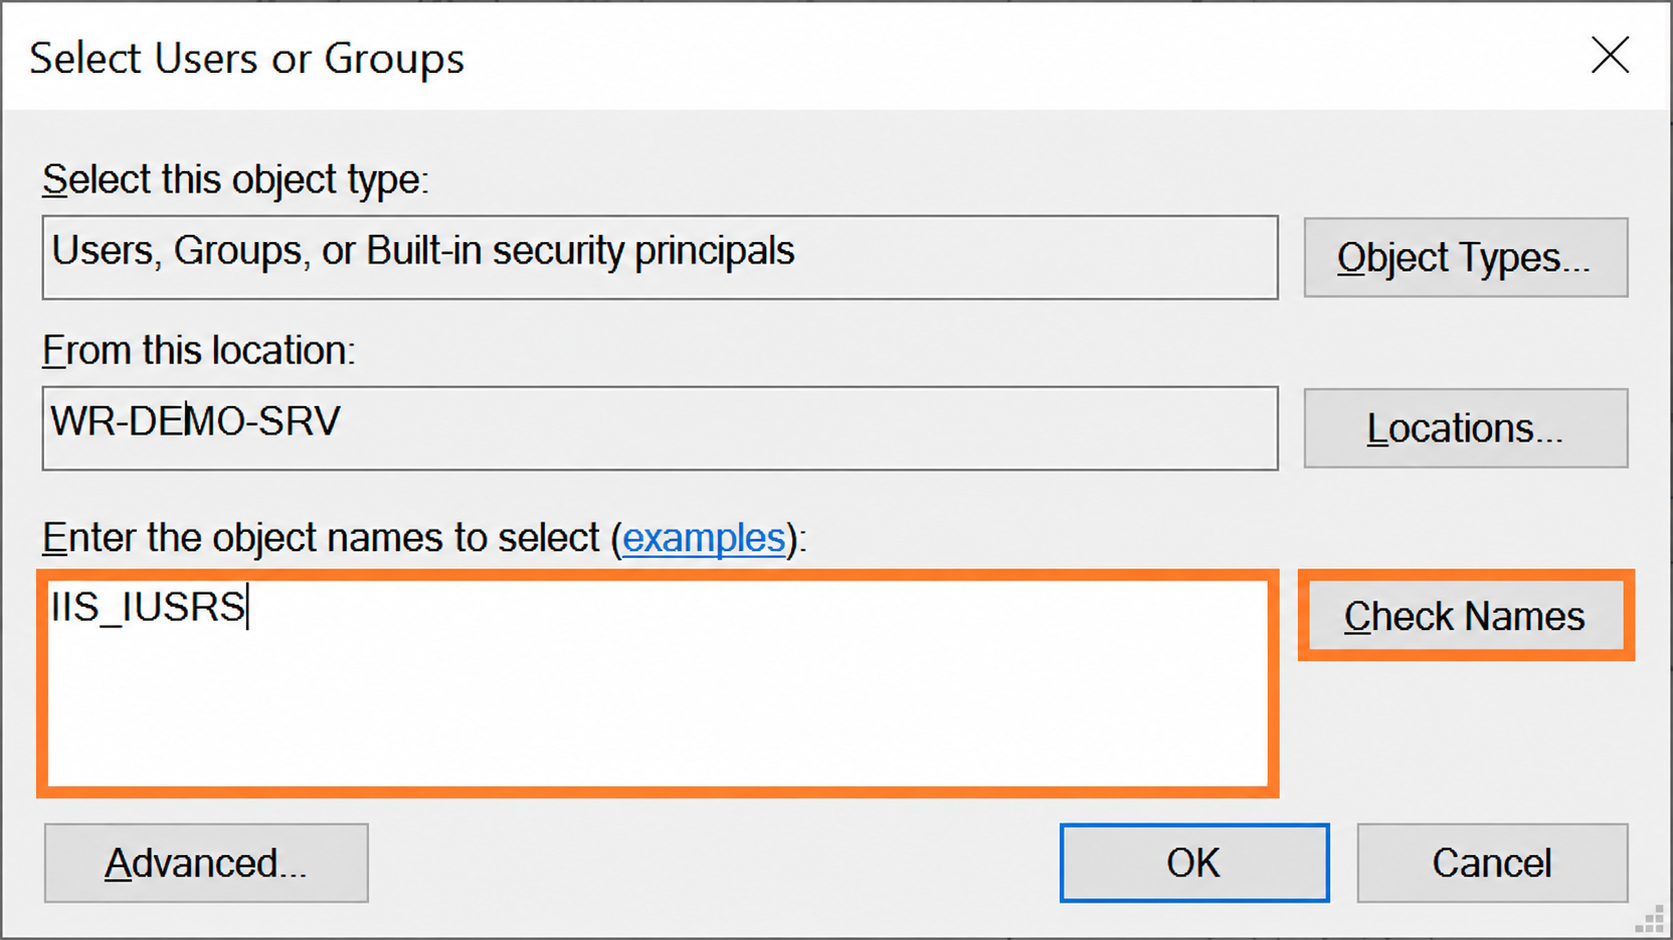
Edited demo reference before Check Names: use the local server location and enter IIS_IUSRS exactly. Select the image to view it at full size.
If Check Names cannot resolve the group, verify the spelling, local server location, and IIS installation. Do not create a similarly named group as a substitute.
Configure Permissions
- Confirm the Object name is the intended WebReports application folder.
- Select IIS_IUSRS under Group or user names.
- In the Allow column, select Full control. Windows also selects the related permissions. Leave the Deny column unchanged.
- Select Apply, then OK to save.
- Reopen Properties → Security → Advanced. Review the IIS_IUSRS permission entry and confirm Full control applies to This folder, subfolders and files.
- Close the dialogs after verifying the saved entry.
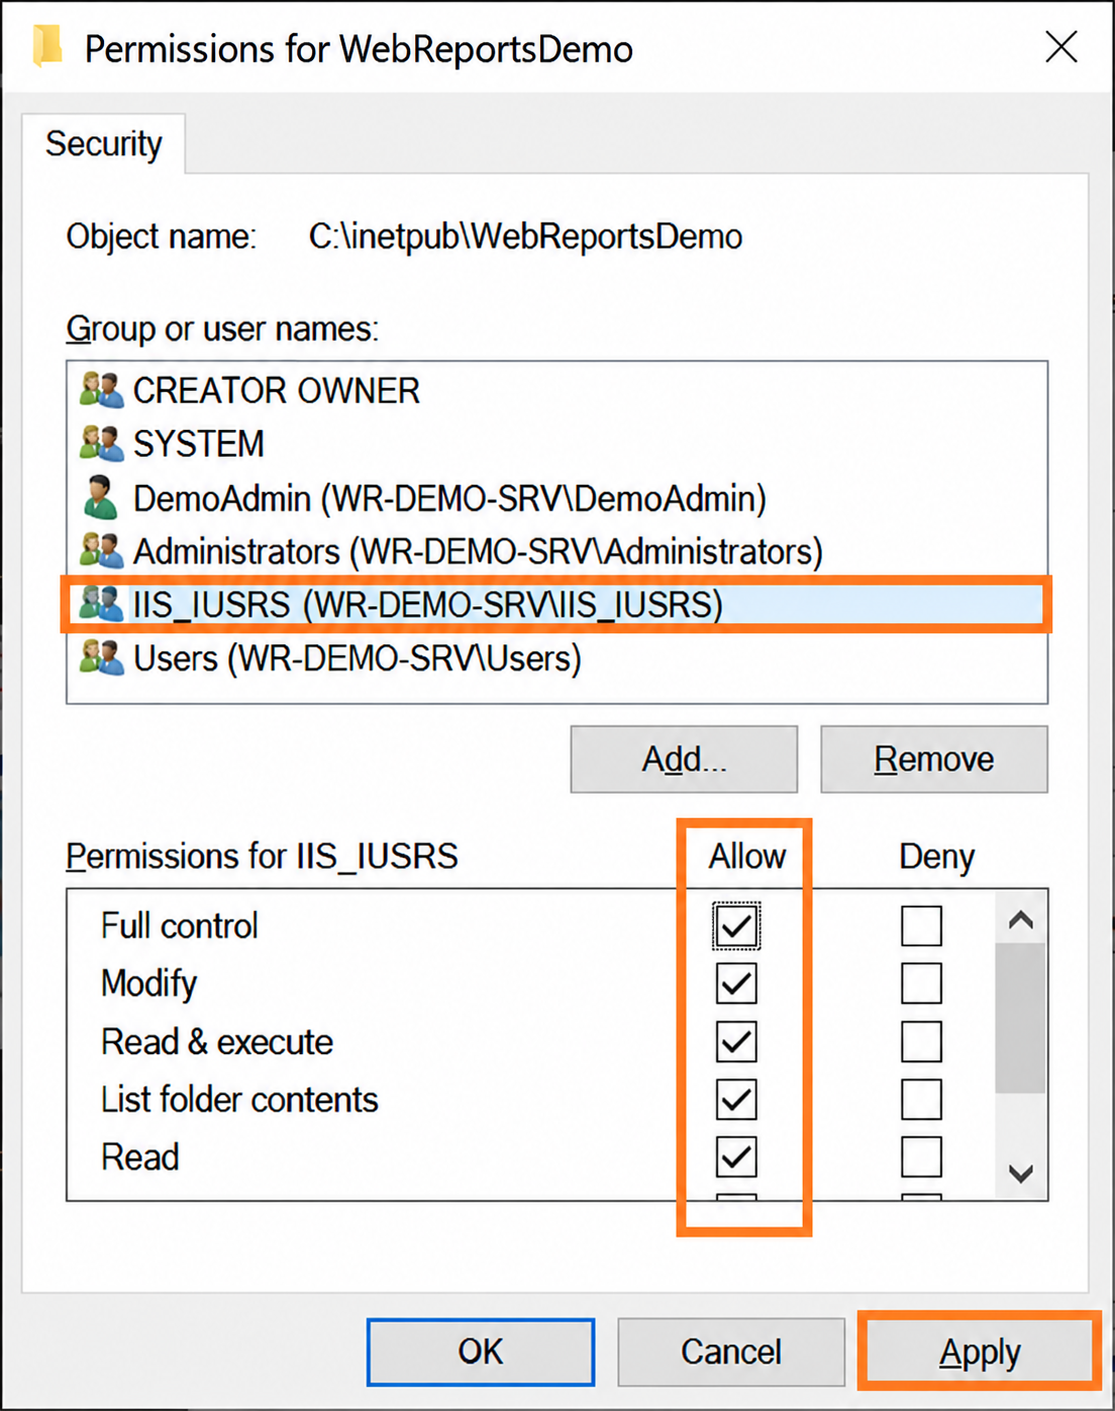
Edited demo reference: select IIS_IUSRS and Allow Full control, then Apply to save. This illustrates the choice before saving; verify the saved folder and inheritance scope on your own server. Select the image to view it at full size.
Keep the existing SYSTEM, Administrators, and other required permission entries. If a child folder or file has inheritance disabled or an explicit Deny entry, have the administrator review that object's effective access rather than assuming the parent grant reached it. Review exceptions individually before replacing existing child permissions.
If this deployment stores application files or writable data outside the site's physical directory, review those actual destinations separately with the administrator. A grant on the WebReports folder does not establish access to an unrelated location.
Verify the Permissions
After saving the folder permissions and completing the other deployment settings:
- Start the WebReports application pool and website using the deployment guide. If a restart is needed for an existing installation, coordinate it for the WebReports site and pool.
- Open the configured HTTPS URL and sign in with the prepared WebReports administrator account.
- Confirm the application can create or update its file-based application logs in the location used by this release and deployment. Check for a new timestamp or recorded entry, not just an existing readable file.
- If custom branding is used, use an approved test image, select Configuration → Branding, upload the image, and select Save. Verify the saved result and retain the original branding for restoration when the test is complete.
- Review any access-denied message and its exact file path. Successful sign-in alone does not verify every file-writing operation.
The in-application Logs page is useful for diagnostics, but viewing its records alone does not prove the worker process can write to every required local folder. See WebReports Logs Overview and Customize Branding in WebReports.
If an Operation Still Fails
- Confirm the site's physical path, assigned pool, and current worker identity match the deployment you edited.
- Confirm the local IIS_IUSRS entry was saved with Full control and the intended inheritance scope.
- Review the specific failing file or folder for inheritance exceptions, explicit Deny entries, or a path outside the application directory.
- Check available disk space and whether the file is locked or read-only. A failed write can have a cause other than a missing permission.
- Provide the exact error, path, operation, and WebReports version to the deployment administrator or BridgeWorks Support.
Next Steps
Return to Configure IIS and Deploy WebReports to continue first launch and verification. For the full installation sequence, see Installing WebReports on Windows.
Comments
0 comments
Please sign in to leave a comment.